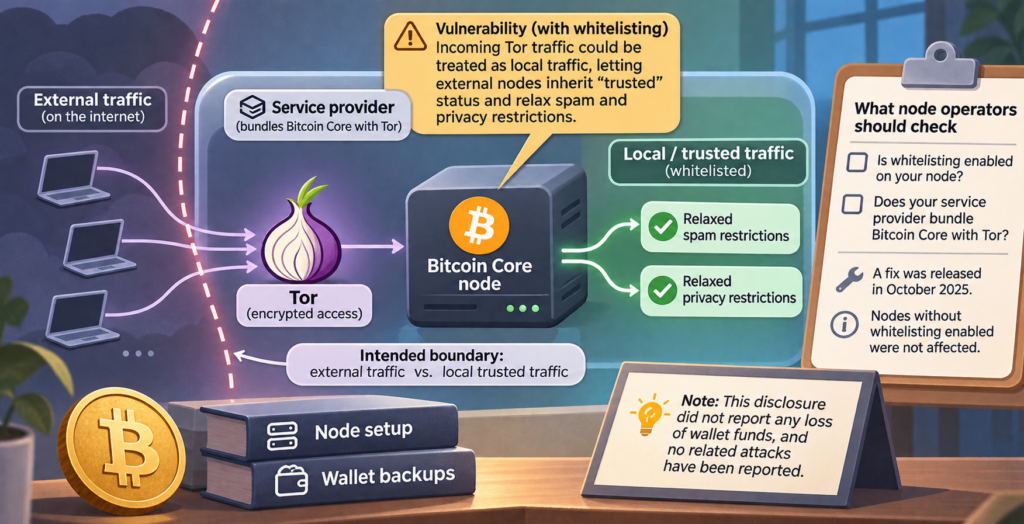
If you rely on a Bitcoin node as part of your long-term holding setup, its network settings deserve attention alongside your wallet backups. A reported Bitcoin Core vulnerability concerned nodes with whitelisting enabled when a service provider bundled Bitcoin Core with Tor—not a reported loss of wallet funds.
In a November 13, 2026 report published at 22:29 (UTC+8), Odaily cited a post by Bitcoin News on X about the Bitcoin Core disclosure. According to that account, incoming Tor traffic could be treated as local traffic. This allowed external nodes to inherit “trusted” status and relaxed spam and privacy restrictions on whitelisted nodes. Bitcoin News said the issue affected thousands of nodes.
The report said a fix was released in October 2025, while details were disclosed two weeks after Bitcoin Core ended support for the 29.x series. It also described a separate, high-severity vulnerability that could prevent mining nodes from constructing valid blocks until restarted. No related attacks had been reported, according to the report, and nodes without whitelisting enabled were not affected.
For node operators, the practical check supported by this disclosure is whether whitelisting is enabled and whether a service provider bundles the node with Tor. The report does not identify wallet losses or provide a basis for treating every Tor-connected node as affected.