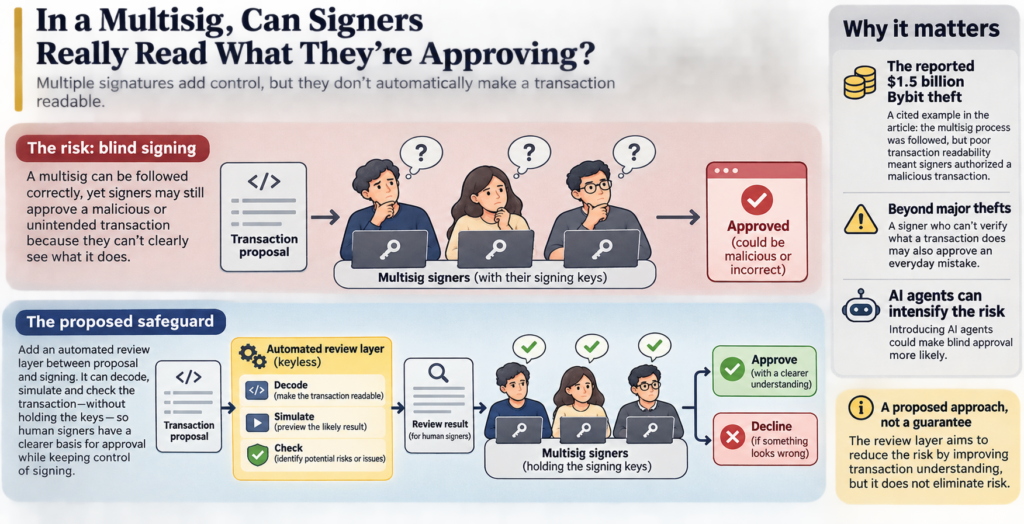
For long-term holders, a multisig wallet raises a practical question: can each signer understand the transaction before approving it? A June 5, 2026 article on blind signing argues that the answer is often no. Requiring multiple signatures does not, by itself, make a transaction readable.
The article points to the reported $1.5 billion Bybit theft as an example. Its account is that the multisig process was followed, but poor transaction readability meant signers authorized a malicious transaction. The concern extends beyond a catastrophic theft: a signer who cannot verify what a transaction does may also approve an everyday mistake. The article warns that introducing AI agents could intensify this problem.
Its proposed safeguard is an automated review layer between proposal and signing. That layer would decode, simulate and check a transaction without holding the keys. The aim is to give human signers a clearer basis for approval while leaving control of signing with them. It is a proposed approach, not an assurance that review would eliminate risk.