If you have contacted Coinone’s customer support, be alert to messages that refer to details from that conversation. In its November 15, 2026 disclosure, the South Korean crypto exchange warned that such details could be used to impersonate it after an attacker accessed servers run by its outsourced support provider, MetaM.
Coinone said the attacker viewed or extracted support records on November 12, and that it learned of the breach the same day. Depending on what a customer shared, potentially exposed information included names, phone numbers, email addresses, dates of birth, bank account numbers, passwords, national identification numbers, home and wallet addresses, and transaction IDs. Coinone did not say how many customers were affected; it said people who had never contacted its support center were unaffected.
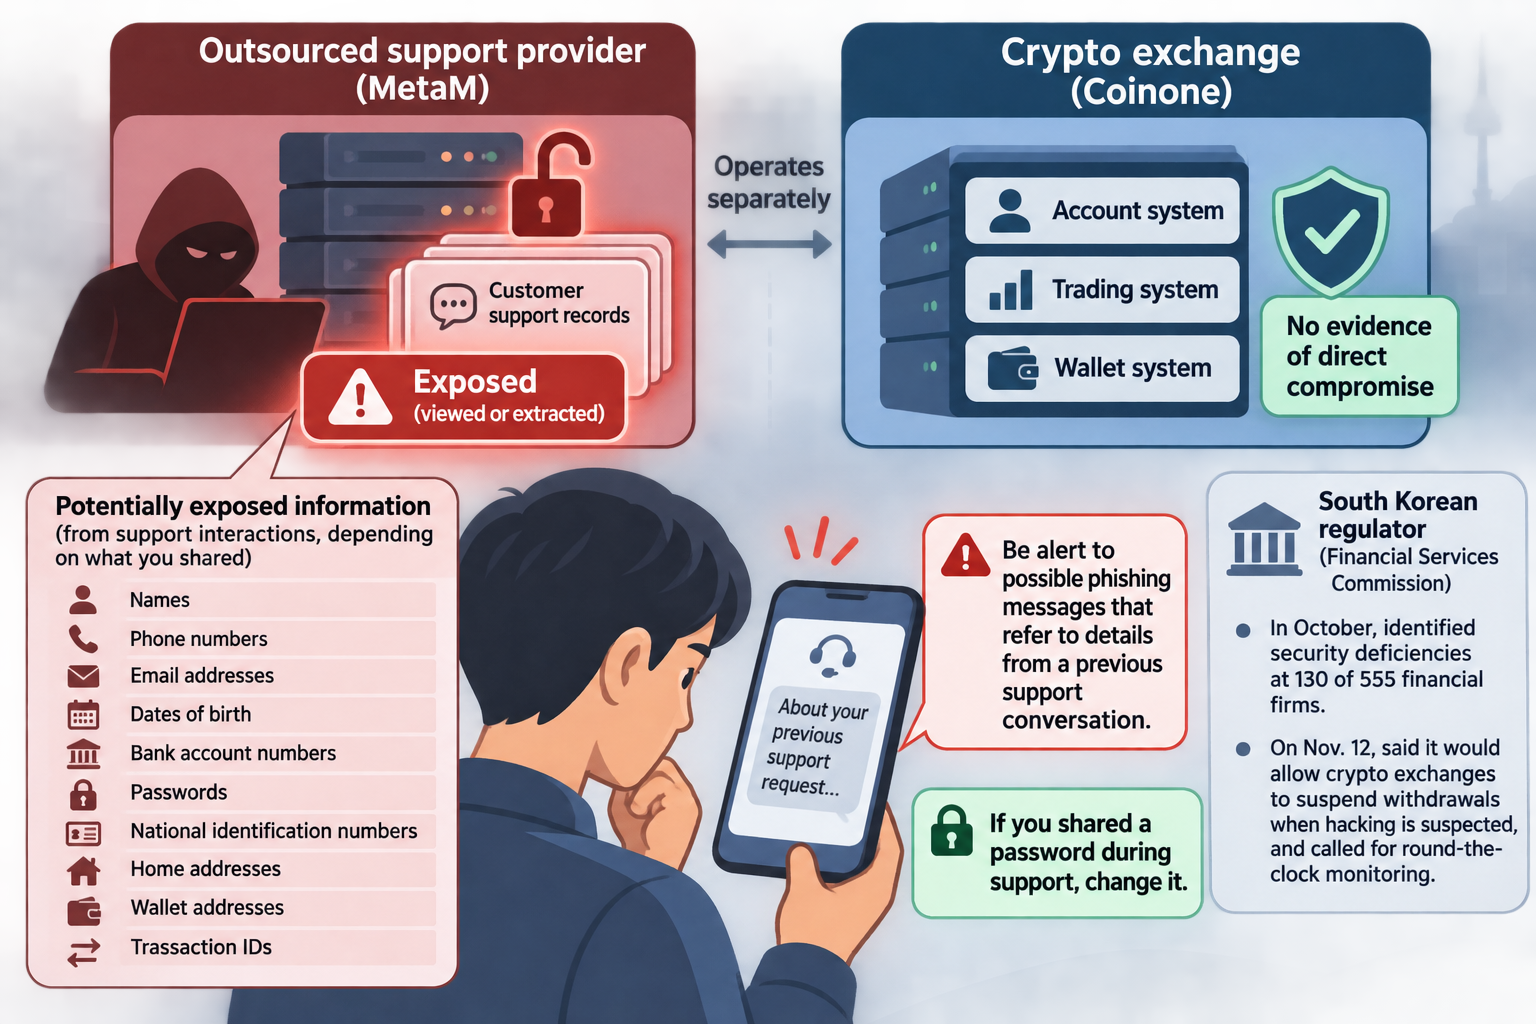
The exchange urged anyone who shared a password during a support interaction to change it. It also warned that a fraudulent message could appear credible by referring to a previous conversation. Coinone said its account, trading and wallet systems operate separately from MetaM’s servers and that it had no evidence those systems were directly compromised. It said it reported the incident to South Korean authorities.
The disclosure followed an October review in which South Korea’s Financial Services Commission identified security deficiencies at 130 of 555 financial firms. On November 12, the regulator said it would allow crypto exchanges to suspend withdrawals when hacking is suspected and called for round-the-clock monitoring. That statement described a prospective measure, not a withdrawal suspension at Coinone.