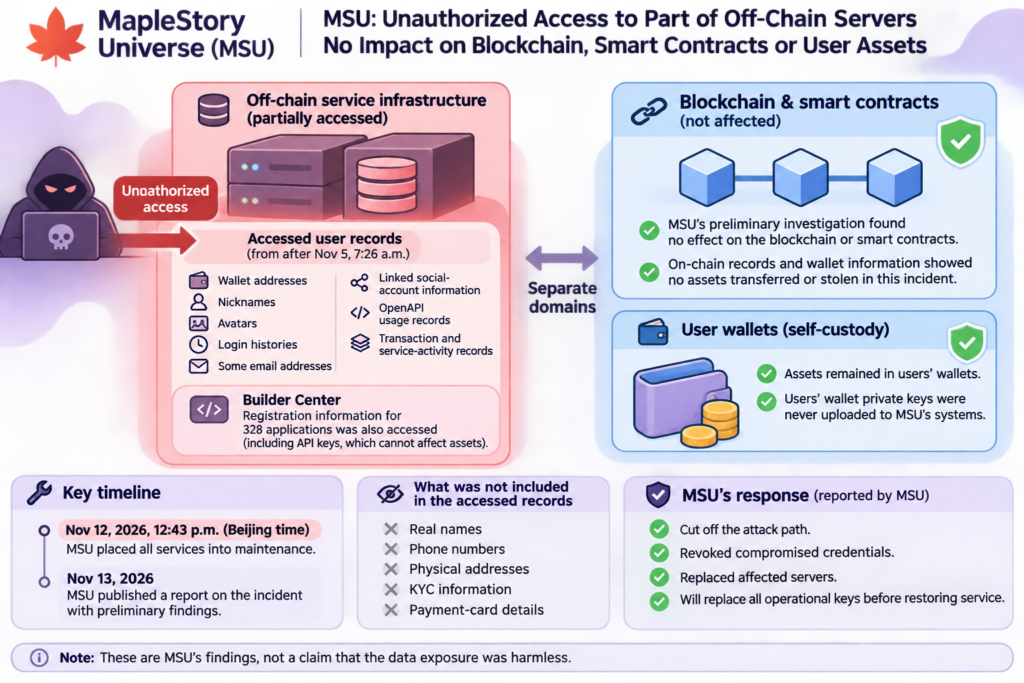
For anyone holding assets in a wallet, this incident draws a distinction between wallet custody and the personal information a service may hold. In a report published on November 13, 2026, MapleStory Universe (MSU) said it had found unauthorized access to part of its off-chain server infrastructure. It placed all services into maintenance at 12:43 p.m. Beijing time on November 12.
MSU said its preliminary investigation found no effect on the blockchain or smart contracts. According to MSU, on-chain records and wallet information showed no assets transferred or stolen in this incident, and users’ wallet private keys were never uploaded to its systems. Those are MSU’s findings, not a claim that the data exposure was harmless.
The attacker accessed some user records dating from after 7:26 a.m. on November 5, MSU said. The records included wallet addresses, nicknames, avatars, login histories, some email addresses, linked social-account information, OpenAPI usage records, and transaction and service-activity records. MSU said they did not include real names, phone numbers, physical addresses, KYC information or payment-card details.
Registration information for 328 applications in Builder Center was also accessed. MSU said the exposed API keys could not affect assets. It reported that it had cut off the attack path, revoked compromised credentials and replaced affected servers, and said it would replace all operational keys before restoring service.