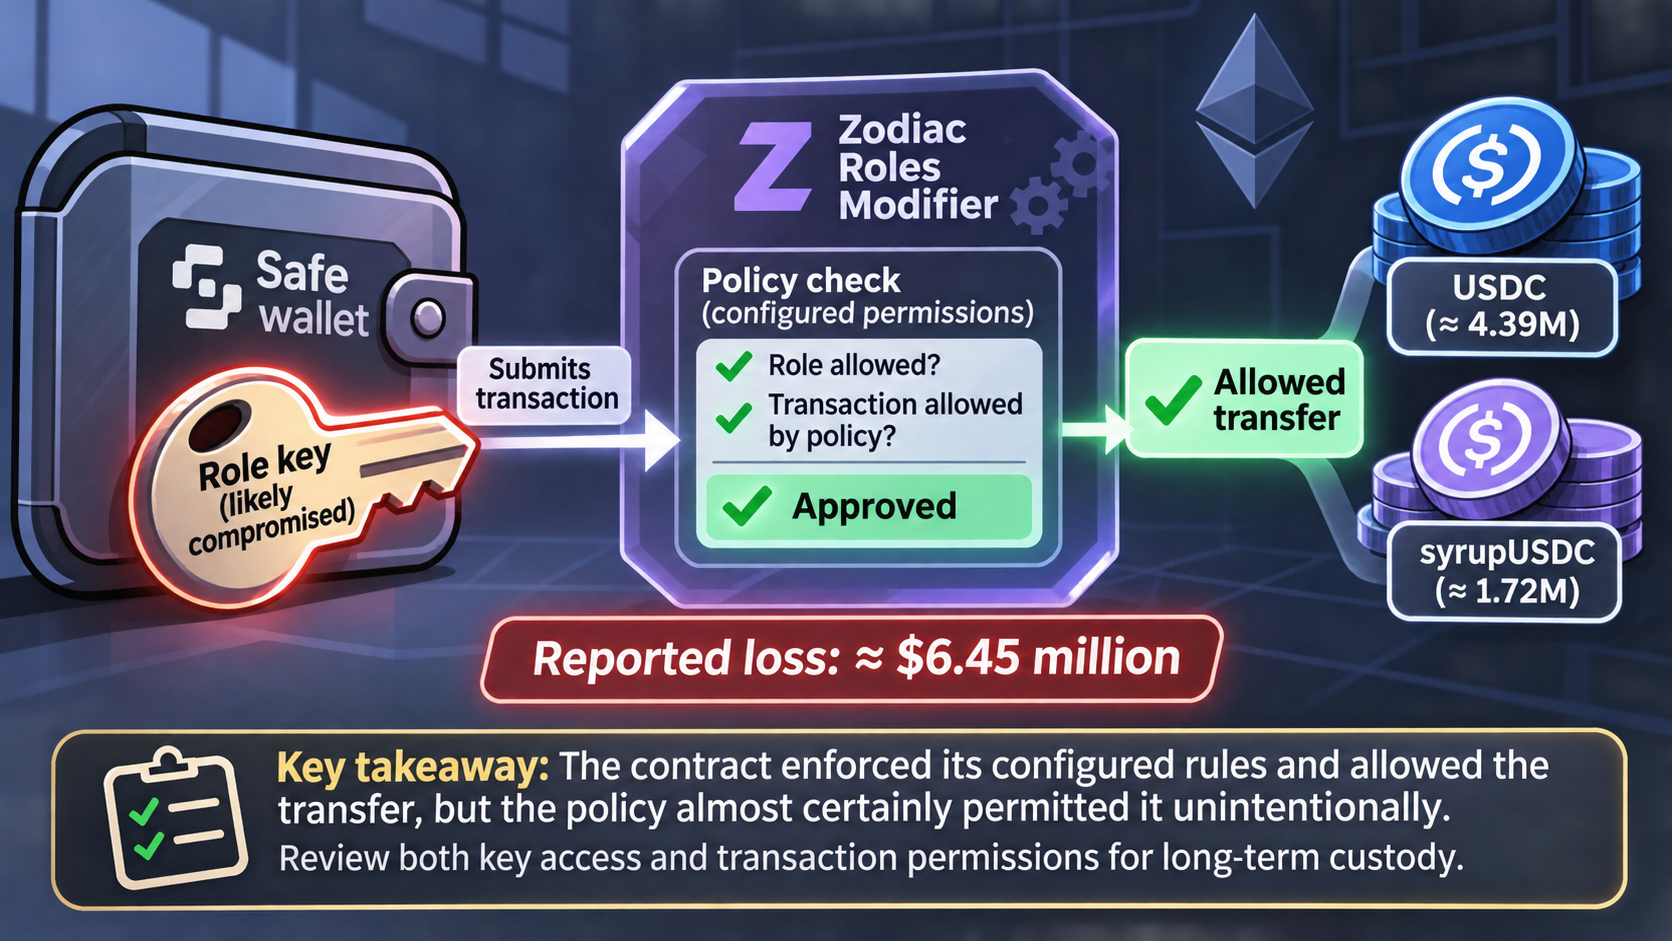
For anyone holding crypto in a wallet with delegated transaction permissions, the question is not only who controls the keys, but what those keys are allowed to do. In reporting published on November 17, 2026, a Safe wallet was reported to have lost about $6.45 million. Zodiac’s co-founder said the transaction was permitted by the wallet’s configured policy and most likely came from a compromised key—not a vulnerability in Zodiac’s contracts.
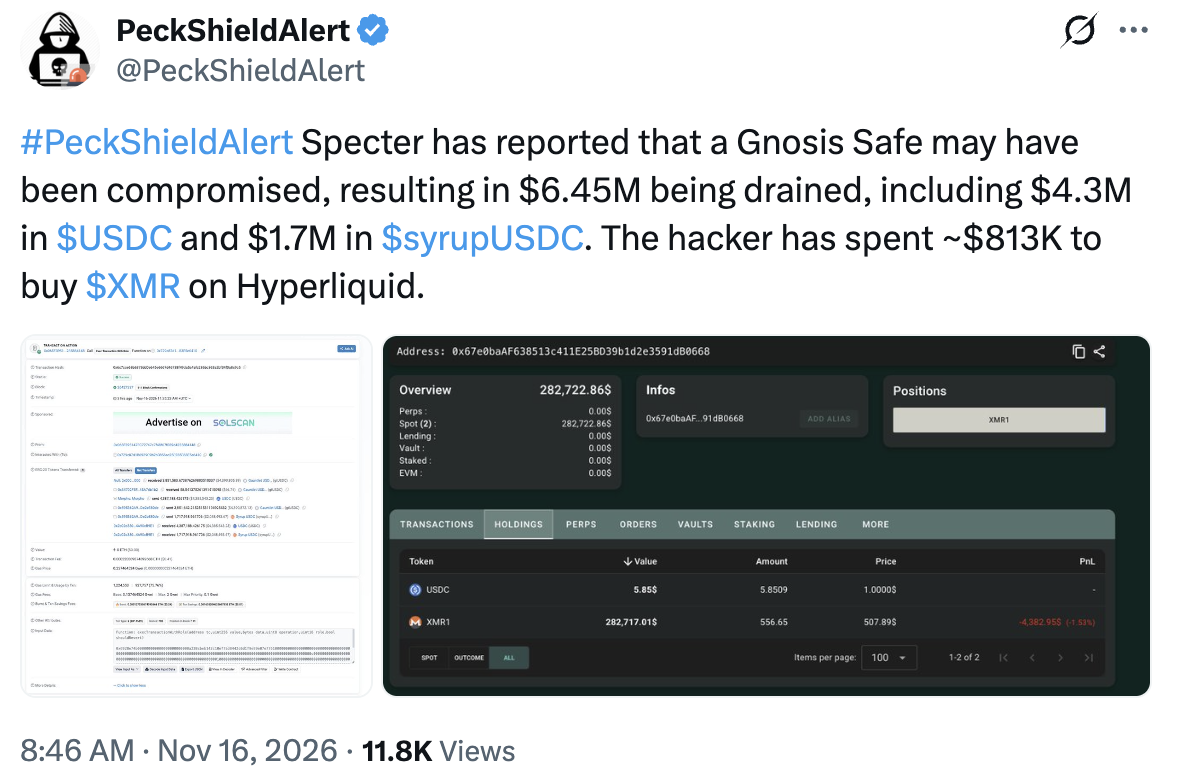
Ethereum records reviewed by Cointelegraph showed approximately 4.39 million USDC and 1.72 million syrupUSDC tokens leaving the wallet in a single transaction on November 16. Security firm PeckShield reported the suspected theft, citing onchain investigator Specter, who had flagged the Zodiac Roles module as part of the suspected attack.
Zodiac co-founder Johannes Moormann said his team reviewed the transaction and confirmed that it passed through the wallet’s Zodiac Roles Modifier. The module checked the transfer against the configured permissions and allowed it. Moormann said the policy almost certainly permitted the transfer unintentionally. He also said the wallet’s operators controlled its keys and permissions; Zodiac had no access to them and was not involved in their setup. Zodiac had not been in contact with the affected team, and the wallet owner’s identity had not been established. Cointelegraph had received no response from Safe or Gnosis Guild by publication.
PeckShield said the attacker used approximately $813,000 to buy Monero-linked tokens on Hyperliquid. Separately, analytics firm Bitquery traced funds through multiple addresses to Hyperliquid, where it said five accounts bought approximately $1 million in XMR1 tokens. Bitquery noted similarities to fund movements following a November 16 Lighter incident, but found no transfers connecting the two wallet groups and could not establish whether the same actor was involved.
The practical distinction is between a contract enforcing its configured rules and those rules matching the operator’s intentions. This report does not establish a flaw affecting other wallets using Zodiac Roles. It does show why reviewing both key access and transaction permissions matters for long-term custody.