For anyone holding assets in a vault, the sBOLD incident is a reminder that a token approval can remain a security risk even when the protocols a vault uses have not themselves been exploited.
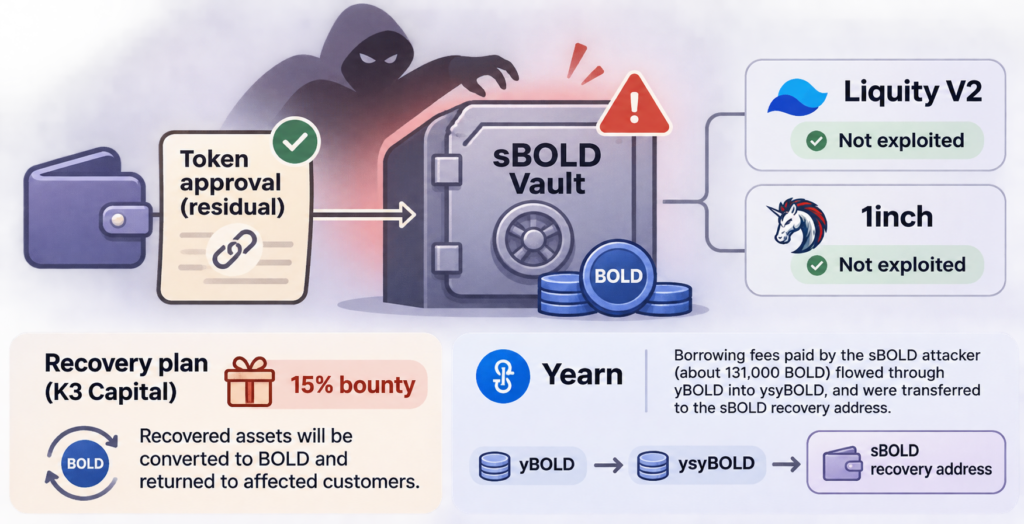
In its account of the November 18, 2026 attack, K3 Capital said an attacker exploited a residual token approval to take approximately 3.43 million BOLD—about $3.43 million—through 99 transactions in roughly 7.5 minutes. K3 Capital said that represented 99.9% of the vault’s assets. It said Liquity V2 and 1inch were not themselves exploited.
According to K3 Capital, the attacker spent approximately 986 ETH competing for transaction ordering, an amount worth more than half the stolen funds. Nearly all of that expenditure went to validator fee recipients, the firm said.
As reported on November 20, 2026, K3 Capital was coordinating recovery and offering a 15% bounty to parties that return funds. It said recovered assets would be converted to BOLD and returned to affected customers. The plan does not establish how much will ultimately be recovered.
Separately, Yearn said approximately 131,000 BOLD in borrowing fees paid by the sBOLD attacker flowed through yBOLD into ysyBOLD. Yearn said it transferred those funds to the sBOLD recovery address and that user deposits and normal earnings were unaffected.