For anyone holding assets on an exchange, the immediate question after a security incident is what happened to customer funds—and what evidence supports the platform’s response.
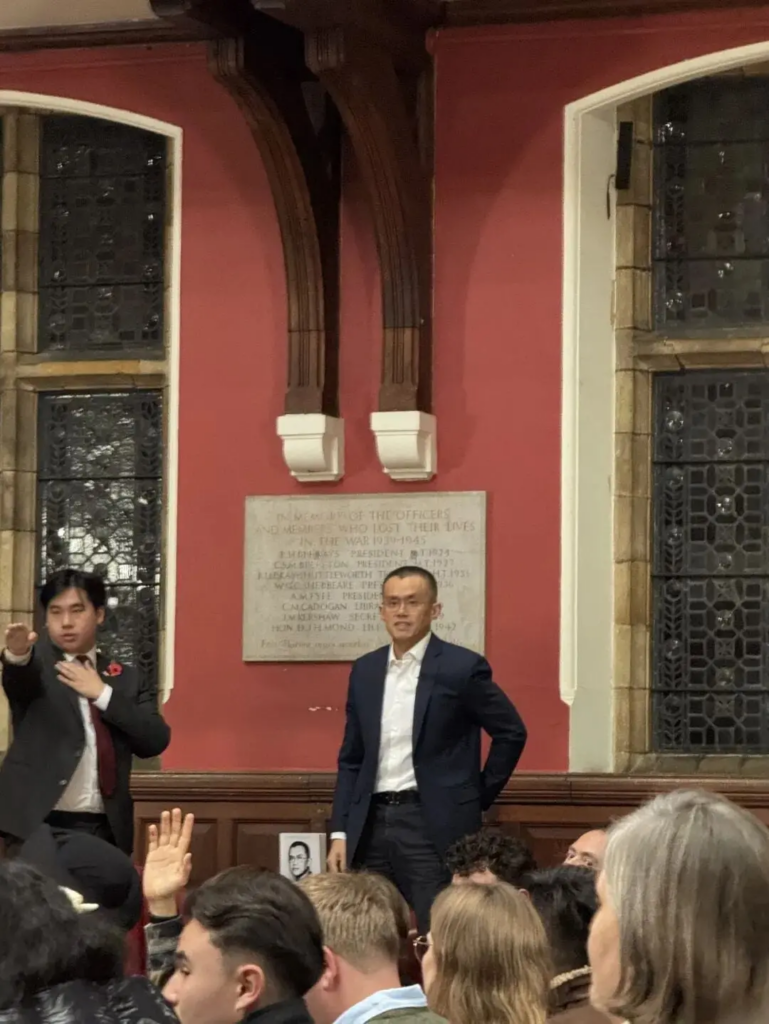
At an Oxford Union discussion on November 3, 2026, Binance founder Changpeng Zhao (CZ) faced that question before an audience of hundreds. As reported on November 6, 2026, the discussion followed a major incident. Binance’s November 3 investigation update said approximately $6.34 billion in digital assets was involved and that about $2.85 billion in related assets had been frozen or intercepted by the time of that update. The amount involved should not be read as a confirmed loss.
What Binance said it would cover
CZ acknowledged shortcomings in Binance’s security and operations, saying the platform could not excuse them by describing the attack as sophisticated. He said Binance would bear users’ asset losses rather than pass them on to customers. According to CZ, the response would draw on the SAFU user-asset protection fund, an insurance fund and company funds. He described SAFU’s size in approximate, billion-dollar terms; those funding details were his estimates at the event, not independently audited figures.
CZ declined to promise that an attack could never happen again. He said the attackers may have spent roughly five or six months preparing, using methods including fake recruitment and social engineering to approach people inside the company, then AI to understand its systems more quickly. He also said some basic operational security procedures had not been followed strictly.
What holders can—and cannot—verify
CZ argued that on-chain activity gives outside analysts a way to identify anomalies, sometimes before a platform does. That visibility can help people assess a response, but it does not by itself verify every claim about frozen funds, reimbursement or internal controls. His distinction between the ability to transfer assets on-chain and the role of a centralized custodian also matters: a transfer’s technical possibility does not remove the platform from the real-world custody and legal picture.
The practical question left by the Oxford discussion is not whether any platform can promise perfect security. It is whether its disclosures, recovery claims and treatment of affected users can be checked as the response continues.