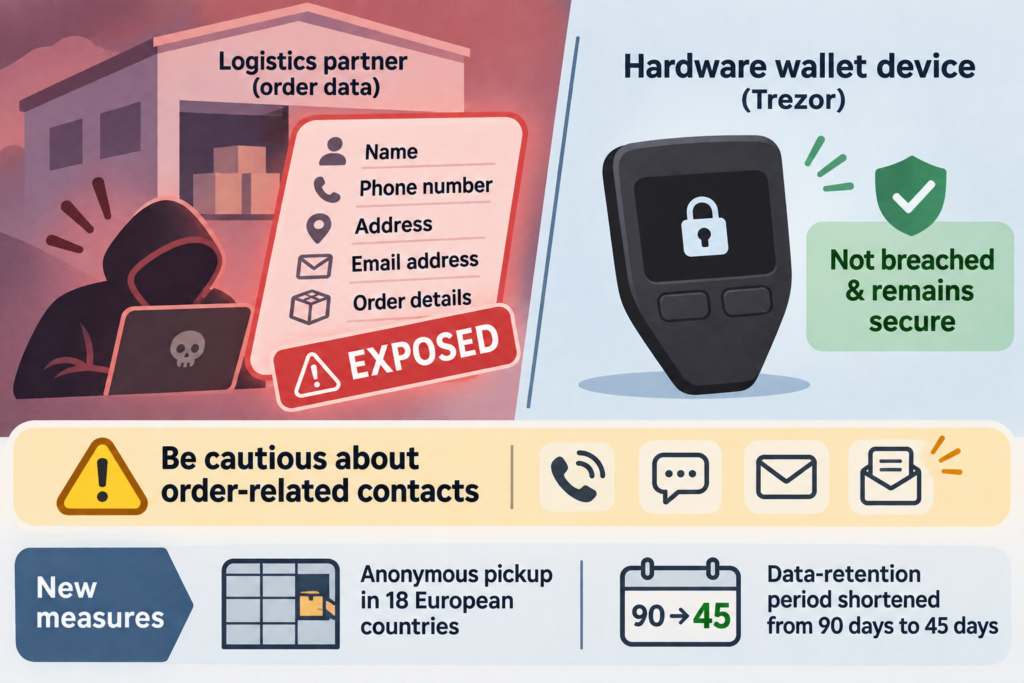
If you ordered a Trezor device, be cautious about messages or calls that refer to your order. In a report published on November 17, 2026, PANews said Trezor had disclosed unauthorized access to customer order data held by its logistics partner, Skladon.
According to Trezor, Skladon notified it on November 15. Data from an estimated 27,000 orders placed between August 9 and November 7 was exported, including names, phone numbers, addresses, email addresses and order details. Customers in multiple countries were affected, but Trezor said US customers were not.
Trezor said its own systems were not breached and its devices remain secure. The distinction matters: the reported exposure concerns order information, not a reported compromise of the hardware wallets. Trezor urged customers to watch for order-related calls, texts, emails and letters, and to consider personal-safety risks associated with exposed address information.
Trezor also said it had introduced anonymous pickup in 18 European countries and shortened its data-retention period from 90 days to 45 days.
Source: panewslab.com (originally published 2026-11-17 01:43 UTC+8)