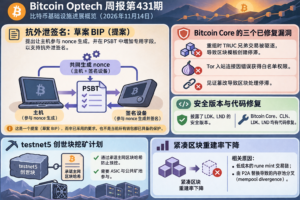
If you use an independent signer to check a wallet’s signatures, the key question is whether both signers produce the same result for the same private key and message. BIP 461, described in material published on November 18, 2026, proposes an ECDSA signing algorithm designed to make that comparison possible.
The proposed algorithm derives the nonce using RFC 6979, applies low-r grinding and normalizes s to a low value. Together, these steps make the signature depend entirely on the private key and message, rather than choices left to the signer. The specification says this would allow two independent signers to cross-check their outputs for signs that a signer is leaking key material.
It also limits a DER-encoded signature to 70 bytes, or 71 bytes with the sighash byte. The material describes nonce derivation, signing, verification and a DeterministicSign algorithm, and discusses backward compatibility with existing consensus rules and a reference implementation. These are properties of a proposed specification, not a claim that wallets have adopted it.