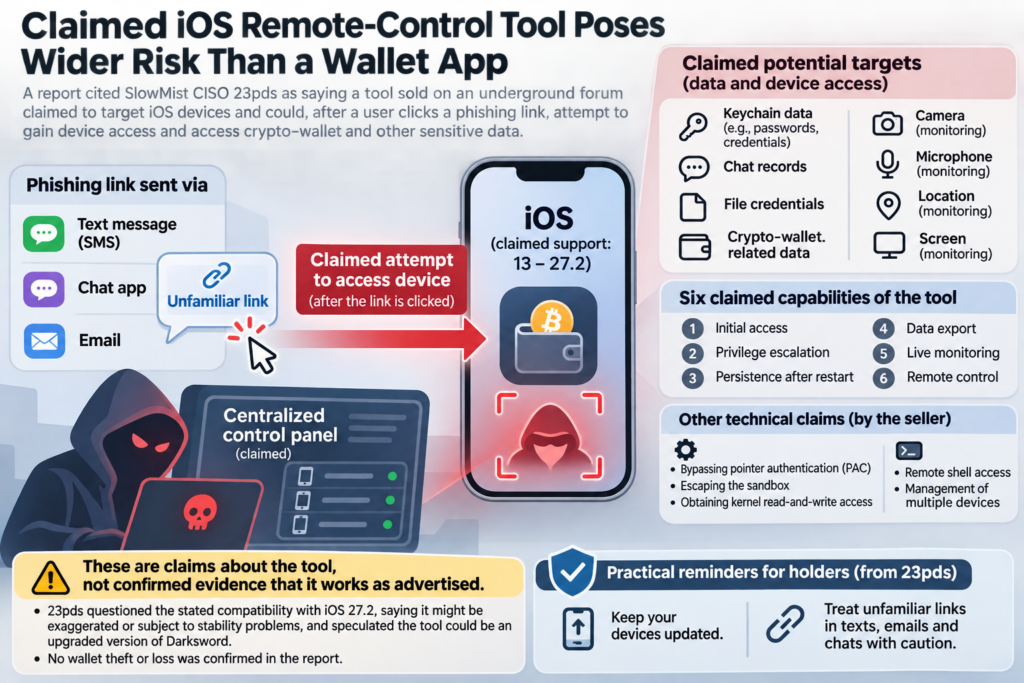
A link opened on a device used to manage crypto could put more than the wallet app at risk. In a report published on November 15, 2026, ChainCatcher cited SlowMist CISO 23pds on a remote-control tool being offered on an underground forum. The seller claimed it supported iOS 13 through 27.2 and included a centralized control panel.
According to the report, attackers could send phishing links by text message, chat app or email, then attempt to gain device access after a recipient clicked. The tool was claimed to be capable of extracting Keychain data, chat records, file credentials and crypto-wallet-related data. Its advertised capabilities also included monitoring the camera, microphone, location and screen, as well as remote shell access and management of multiple devices.
The seller described six capabilities: initial access, privilege escalation, persistence after restart, data export, live monitoring and remote control. The claims also referenced bypassing pointer authentication (PAC), escaping the sandbox and obtaining kernel read-and-write access. These are claims about the tool, not confirmed evidence that it works as advertised.
23pds questioned the stated compatibility with iOS 27.2, saying it might be exaggerated or subject to stability problems, and speculated that the tool could be an upgraded version of Darksword. No wallet theft or loss was confirmed in the report. For holders, the practical reminder from 23pds was to keep devices updated and treat unfamiliar links in texts, emails and chats with caution.