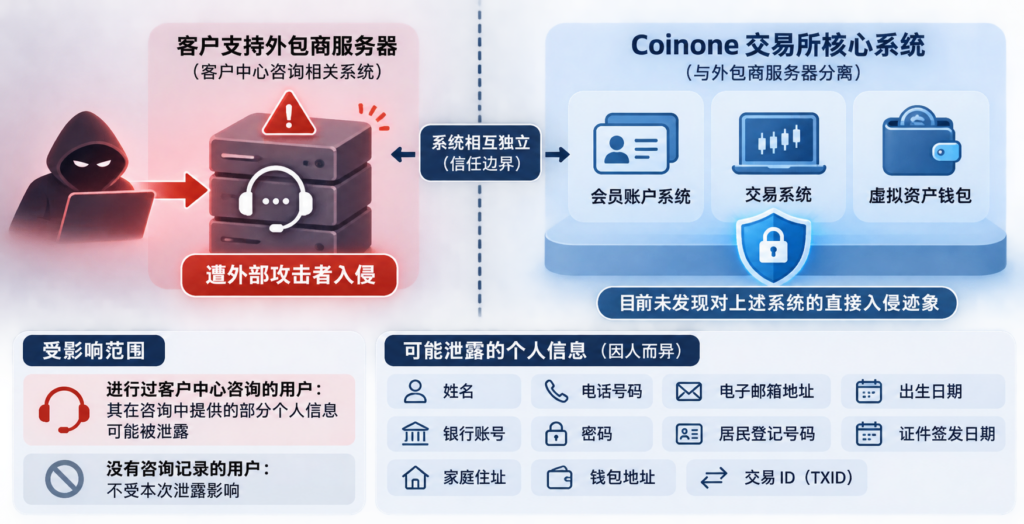
If you contacted Coinone’s customer center, information you shared during that inquiry may have been exposed. According to Coinone, an external attacker broke into a server operated by its customer-support contractor early on November 12, 2026. The exchange said only users with a customer-center inquiry record were affected; users without one were not affected by this breach.
The information potentially exposed varies by person. Coinone listed names, phone numbers, email addresses, dates of birth, bank account numbers, passwords, resident registration numbers, ID issuance dates, home addresses, wallet addresses and transaction IDs (TXIDs) among the possible data.
For holders, the distinction is between support records and custody systems. Coinone said its member accounts, trading systems and virtual-asset wallets are separate from the contractor’s server, and that it had found no signs of a direct intrusion into those systems at the time of its statement. That is not a claim that every customer’s support information was exposed—or a guarantee that no other risk exists. Anyone who contacted support can consider what personal information they provided in that exchange.
Source: panewslab.com (originally published 2026-11-15 11:19 UTC+8)