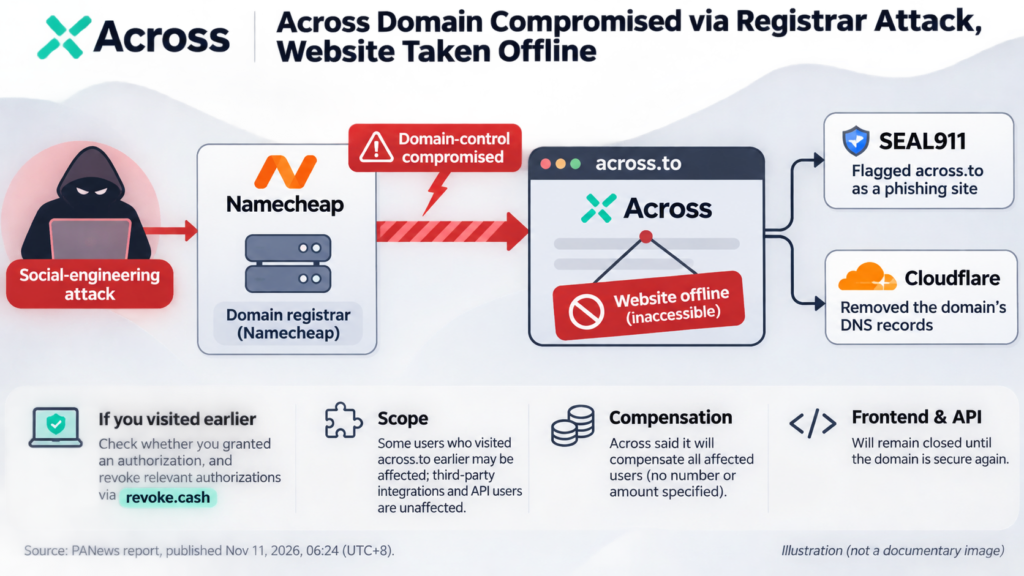
If you visited Across’s website before it was taken offline, the immediate concern is whether you granted an authorization through the site. Across advises potentially affected users to revoke relevant authorizations through revoke.cash.
In a PANews report published on November 11, 2026, at 06:24 Beijing time, Across said its domain registrar, Namecheap, had been targeted in a social-engineering attack at around 02:45 that morning. According to Across, the attacker gained control of its domain. The team received an alert within 15 minutes and began shutting down the website.
Across said SEAL911 subsequently flagged across.to as a phishing site and Cloudflare removed the domain’s DNS records, leaving the phishing site inaccessible. Some people who had visited across.to earlier may have been affected; Across said third-party integrations and API users were unaffected. It also said it would compensate all affected users, without specifying a number or amount in the report.
Across said its frontend and API would remain closed until the domain was secure again. The report did not establish whether any user funds were lost.
Source: panewslab.com (originally published 2026-11-11 06:24 UTC+8)