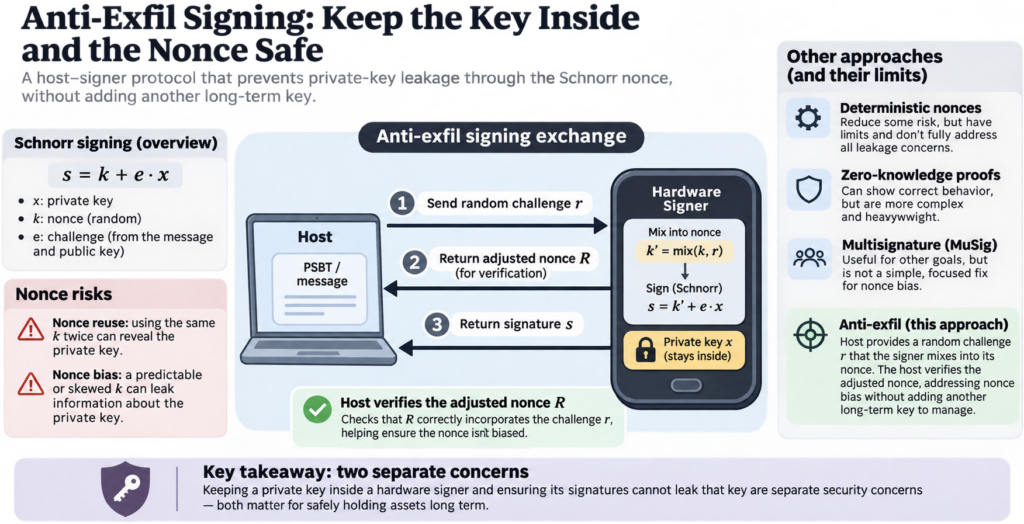
A hardware signer can keep a private key inside the device yet still put it at risk through the signatures it produces. A transcript of Andrew Poelstra’s Silicon Salon IV talk, published on November 15, 2026, explains how a signer could leak private-key information through the nonce used in a Schnorr signature.
The talk starts with the Schnorr signing formula and the risks of nonce reuse or bias. It also examines the limits of deterministic nonces, zero-knowledge proofs and multisignature approaches. Its proposed anti-exfil approach instead has the host provide a random challenge that the signer mixes into its nonce. The host can verify the adjusted nonce, addressing nonce bias without adding another long-term key to manage.
The transcript also discusses Blockstream Jade’s implementation, PSBT interaction and an earlier use of the approach with OpenTimestamps. For someone holding assets long term, the useful distinction is that keeping a key inside a hardware signer and ensuring its signatures cannot leak that key are separate security concerns.